



Agency bolsters protection of key infrastructure against attacks
PETALING JAYA: The National Cyber Security Agency (Nacsa) has stepped up surveillance of the country’s critical infrastructure, issuing alerts and strengthening preparedness measures amid rising cyberattacks.
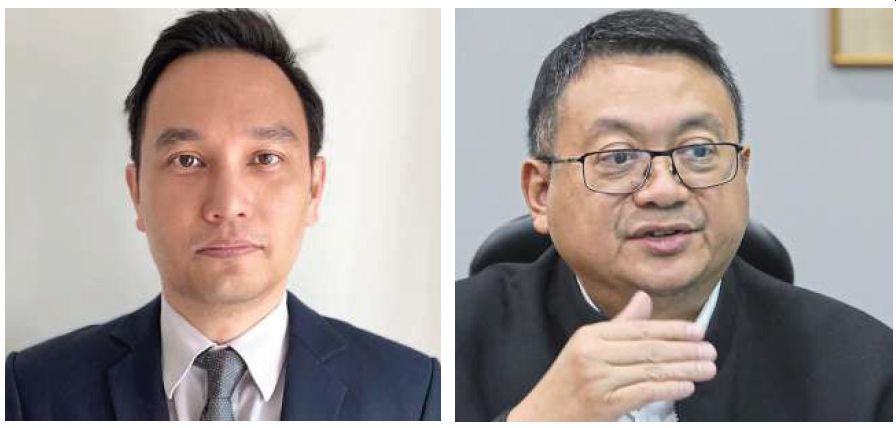
Its chief executive, Dr Megat Zuhairy Megat Tajuddin, said the focus was on ensuring essential services remain resilient against attacks that could disrupt operations, cause economic losses and undermine public trust.
He said the agency, which falls under the National Security Council, was constantly monitoring the situation.
“The National Cyber Coordination and Command Centre (NC4) continuously monitors the cybersecurity situation involving National Critical Information Infrastructure (NCII) entities and government agencies and issues alerts and advisories to help organisations identify and address vulnerabilities before they are exploited,” he told The Star.
The NCII refers to the critical system that includes information assets (electronic), networks, functions, processes, facilities and services in an information and communications technology (ICT) environment that is important to the country.
Any disruption or destruction to NCII will have an impact on national defence and security, national economic stability, national image, the government’s ability to function, public health and safety as well as individual privacy.
Megat Zuhairy said the agency was implementing nine preparedness actions and reporting threat status weekly through respective sector leads.
He said for organisations outside the scope of the Cyber Security Act (Act 854), Nacsa has also issued guidelines setting out 12 priority actions to strengthen their cybersecurity preparedness.
Megat Zuhairy said the risks had extended beyond data theft to disrupting essential services, causing economic losses and eroding public trust.
“Yet, many attacks continue to exploit basic weaknesses, such as unpatched systems, weak passwords and vulnerabilities in suppliers and third parties,” he said.
He said Malaysia’s legal framework was robust and continued to evolve to address these challenges, with two key pieces of legislation serving distinct but complementary purposes.
He said Act 854 focused on prevention, preparedness and resilience, particularly in protecting NCII.
“It establishes clear cybersecurity obligations for NCII entities, including compliance with the relevant Codes of Practice, conducting cybersecurity risk assessments and audits, undertaking cybersecurity exercises, and reporting cybersecurity incidents.
“The objective is to ensure that organisations responsible for critical services have the necessary safeguards and preparedness to manage and respond to cyber threats,” said Megat Zuhairy.
Meanwhile, the Cybercrimes Bill 2026, which was passed in Parliament in July, focuses on addressing cybercrime through the criminal justice system.
“It is intended to modernise the existing legal framework by introducing provisions to address a broader range of cyber offences, including unauthorised access to computer systems, computer-related fraud, identity theft and emerging forms of digital abuse, including AI-enabled deepfakes.
“It will strengthen the legal basis for investigating and prosecuting cyber offences and holding perpetrators accountable,” he said.
Megat Zuhairy, however, acknowledged that laws alone are not enough, adding that it was only as strong as its implementation.
“Ultimately, real resilience depends on organisations translating regulatory requirements into effective security measures and operational readiness. It also requires close cooperation between government, industry and the public. Cybersecurity is a shared responsibility,” he added.
In the most recent incident, the LED screens in Kluang and Bandar Sunway were hacked where inappropriate and obscene content was displayed.
Fellow of the Academy of Sciences Malaysia and former CEO of Cybersecurity Malaysia Datuk Dr Amirudin Abdul Wahab said laws alone could not solve the problem.
There must also be the ability to investigate and prosecute transnational cybercriminals, accountability of organisations and their third-party technology providers, and effective enforcement of existing laws.
“Cybercrime is borderless. Attackers may operate from another country, use infrastructure in several jurisdictions and conceal their identities through multiple layers of technology.
“This requires stronger international cooperation and faster mechanisms for sharing digital evidence,” he said.

